Skip to content

SolutionsSecure & Connect

Secure your hybrid
workforce.

Eliminate the technical debt of legacy VPNs. We partner with senior engineering teams to design Zero Trust architectures that are secure, scalable, and free from vendor lock-in.

Replace Legacy VPN
ZTNA
Device-Level Protection
WARP
Aware Access Policies
Identity

The "castle-and-moat" era is over.

Internal apps are moving to the cloud and users are working from everywhere. Backhauling traffic through a centralised VPN creates bottlenecks and exposes your entire network.

VPN Model

Lateral Movement Risk

Legacy VPNs trust users once they're "inside". A single compromised laptop becomes a gateway to your entire infrastructure.

  • High Risk
  • Broad Network Access
Zero Trust Model

Microsegmentation

Parsectix implements Least Privilege. We verify identity and posture for every request, ensuring users only see what they need.

  • Secure
  • Precise App Access

The Parsectix Methodology

How we migrate you from VPN to SASE.

We use a proven 3-phase framework to transition your workforce without disruption.

  1. Phase 01The "Light Branch" Phase

    Connect & Secure

    We deploy the WARP Client to employee devices and establish lightweight IPsec tunnels from your offices. This secures DNS and encrypts traffic without hardware.

  2. Phase 02Remove the Bottleneck

    Offload VPN

    Parsectix identifies your heaviest internal apps and exposes them via Cloudflare Tunnel. Traffic routes directly to the application, bypassing legacy VPN concentrators.

  3. Phase 03Zero Trust Enforcement

    Context Policy

    We integrate your IdP (Okta/Azure) and Endpoint Protection. Policies shift from "Network Allow" to "User X with Healthy Device Y can access App Z".

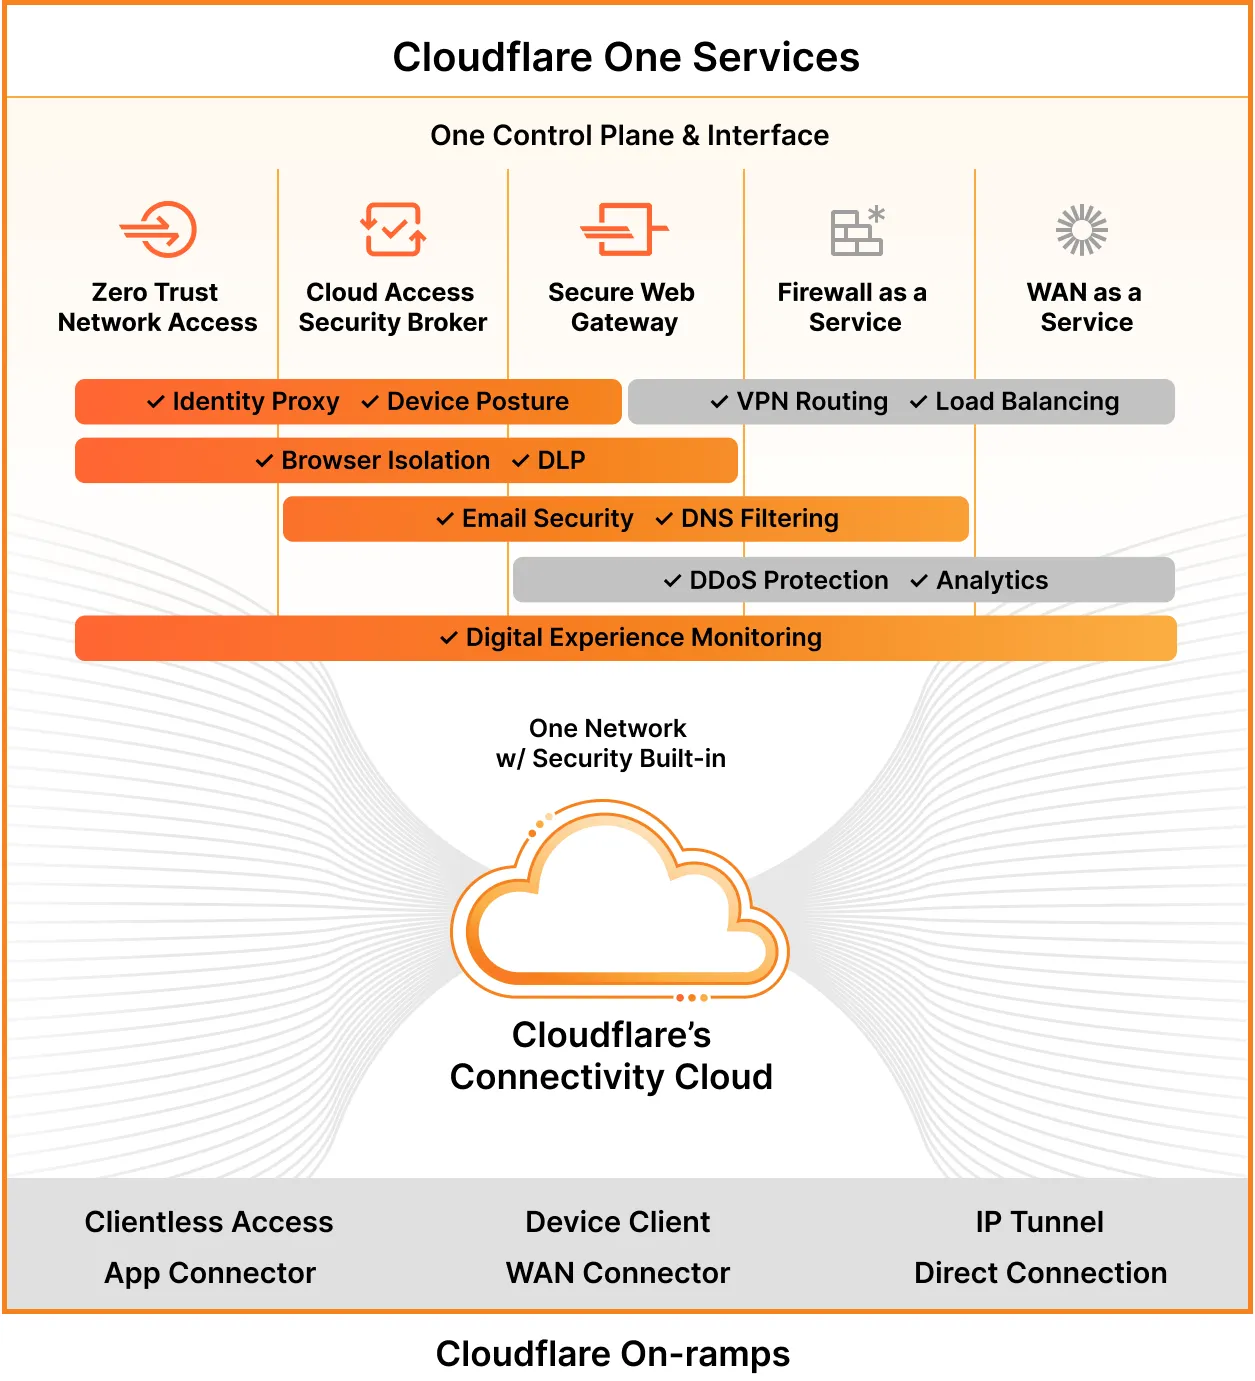
The Cloudflare One platform.

A unified control plane that verifies, filters, and isolates traffic at the edge.

1. Identity & Access Control

  • Connect & Verify
    Users connect via the WARP Client or browser. We integrate with your existing IdP (Okta/Azure AD) to verify identity for every request.
  • Assess Posture
    We check device health (Disk Encryption, CrowdStrike status) before granting access. Risk-based access ensures only healthy devices get in.
  • Enforce Policy
    Traffic hits the Global Edge where granular policies are enforced. Access is granted per-application (Least Privilege).
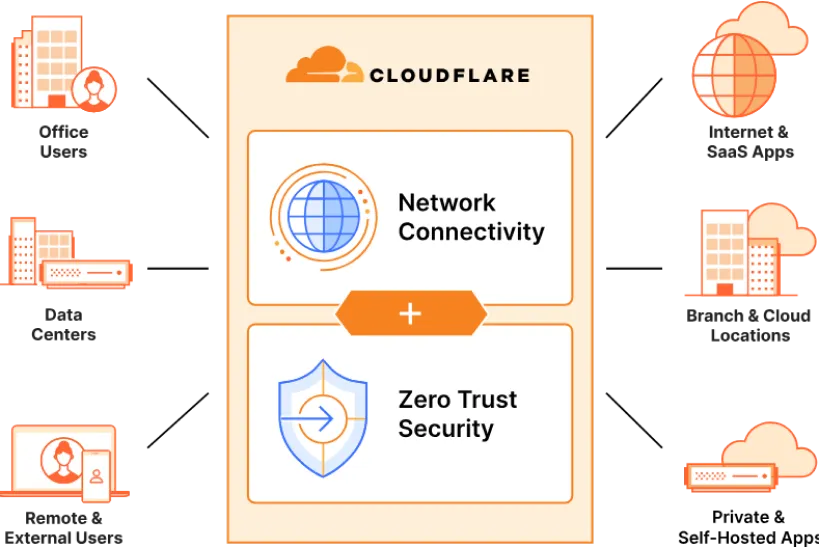
Cloudflare Zero Trust Connectivity Flowchart

2. Threat & Data Protection

  • Secure Web Gateway (SWG)
    Filter and inspect all Internet traffic. Block phishing sites, C2, and enforce AUPs for roaming users legally.
  • CASB & DLP
    Detect sensitive data (PII, Credit Cards) in motion or at rest in SaaS applications. Prevent data exfiltration.
  • Remote Browser Isolation
    Execute risky websites in a remote container at the edge. Protect users from zero-day threats by streaming only pixels.
Cloudflare One SASE Marketecture

Managed zero trust.

We architect, deploy, and manage your SASE transformation so you don’t have to.

Policy "Nerve Center"

We translate your business requirements into granular Gateway and Access policies. We handle the complexity of regex, BPF, and identity rules.

Identity Integration

Seamless synchronisation with Okta, Azure AD, or Google Workspace. We ensure your users' groups and roles map correctly to Zero Trust policies.

Active Policy Enforcement

We continuously monitor unauthorised Shadow IT usage and block malicious domains.

Professional & Managed Services

Why teams partner with Parsectix.

We don’t just resell licences. We engineer, migrate, and manage your Zero Trust transformation.

Professional Services

  • Zero Trust Architecture Design
    Custom tailored policy design aligning with your specific compliance (SOC2, ISO) and security requirements.
  • Legacy VPN Migration
    Carefully planned migration and execution. We handle the complexity of moving apps from VPN concentrators to Cloudflare Tunnel.
  • Identity & Device Integration
    Seamless integration with Okta, Azure AD, and CrowdStrike/SentinelOne for device posture checks.

Managed Services

  • Active Policy Management
    We handle all policy changes, rule tuning, and configuration updates so your internal team doesn’t have to.
  • Lifecycle Management
    Regular policy reviews and updates. We ensure your configuration evolves with your changing team topology.
  • Senior Engineering Support
    Direct access to L3 engineers. No tiered support queues. Just experts who know your architecture.

FAQ

Common questions.

Yes, for the large majority of use cases. Cloudflare Tunnel handles web apps, SSH, RDP, and SMB traffic securely. For the rare legacy protocols (VoIP/SIP), we can maintain a minimised IPsec tunnel as a fallback.

No. We overlay Zero Trust on top of your existing infrastructure. We slowly migrate applications one-by-one, ensuring no disruption to your daily operations.

Cloudflare provides the tool; we provide the engineering. We handle the complex architecture, policy design, and migration execution that internal teams often struggle to resource.

A typical migration takes 4-8 weeks. We start with low-risk internal tools ("Light Branch" phase) to build confidence before cutting over critical infrastructure.

Both. We typically start with a Professional Services migration project, then transition to a Manage & Operate retainer for ongoing policy tuning and support.

We architect high-availability setups. This includes redundant tunnels to multiple Cloudflare datacenters and "Break Glass" bypass mechanisms for emergencies.

Start your Transformation

Secure your hybrid workforce.

Get a free Zero Trust Architecture assessment. We’ll map your applications and design a migration plan.

A 30-minute peer conversation, not a sales pitch.