SolutionsAWS Advanced Partner
Build your
enterprise landing zone
right the first time.
Don’t build on shaky ground. An AWS Landing Zone is your insurance policy against security breaches, compliance failures, and cost overruns. Get it right from day one.
- Automated Provisioning
- AFT
- Preventive Guardrails
- SCPs
- Immutable Audit Trail
- Logs
Why landing zones matter.
The "ClickOps" Trap
Manual account creation and ad-hoc security settings lead to "Security Sprawl." Teams bypass guardrails to move fast, creating hidden vulnerabilities and unmanaged costs.
- Drift & Incompliance
- Surprise Bills
- Provisioning Bottlenecks
The Landing Zone
A precise, automated foundation. Accounts are vended with security baselines baked in. Governance is invisible, audit compliance is automatic, and developers just code, while maintaining quality.
- Automated Policy Enforcement
- Single-Pane Observability
- Self-Service Vending
Three Pillars Framework
Built on AWS best practices.
Every successful landing zone delivers value across three critical dimensions. Here’s how we build yours.
Governance
Centralised control without bottlenecks. Your teams get the autonomy they need within guardrails you define.
AWS Organizations Structure
Hierarchical account organisation with OUs for different environments, teams, and workloads. Logical segmentation that scales with your business.
Automated Account Provisioning
Account Factory creates new accounts in minutes with security baselines, network, and cost controls pre-configured.
Service Control Policies (SCPs)
Guardrails that set maximum permissions organisation-wide. Prevent admins from disabling security services or exposing data.
Cost Management & Budgets
Consolidated billing, budget alerts, and spending limits. Automatic notifications when thresholds are breached.
Business Value
Faster account onboarding, consistent security baselines, and an audit-friendly foundation from day one.
Security
Defence in depth. Every account starts secure and stays secure through automated monitoring.
Preventive Controls
SCPs and RCPs block risky services and enforce encryption before actions happen.
Detective Controls
GuardDuty, Security Hub, and Config continuously monitor for threats. Centralised security dashboard.
IAM Identity Center (SSO)
Single sign-on across all accounts. Least privilege access with no long-term credentials.
Network Segmentation
Transit Gateway hub-and-spoke design. Centralised inspection and VPC isolation.
Immutable Audit Logs
Centralised, tamper-proof CloudTrail logs with MFA-delete protection for compliance.
Encryption by Default
Enforced encryption at rest (KMS) and in transit. Secrets rotation automation.
Business Value
Preventive guardrails designed to support SOC 2 and PCI-DSS controls, with security baselines applied to every new account.
Operational Excellence
Automation over heroics. Infrastructure as code, centralised observability, and predictable operations.
Infrastructure as Code (IaC)
Terraform or CloudFormation for everything. Version-controlled, peer-reviewed infrastructure changes.
Centralised Observability
Cross-account CloudWatch dashboards and log aggregation. Single pane of glass for all operations.
CI/CD Pipelines
Automated deployment pipelines with testing and approval gates. Rollback capabilities.
Disaster Recovery & Backup
Automated AWS Backup policies. Cross-region replication for critical data compliance.
Automated Remediation
Self-healing infrastructure using Config Rules and EventBridge to fix issues automatically.
Runbooks & Docs
Automated documentation and Systems Manager runbooks. Knowledge base that evolves with you.
Business Value
Built for high availability, with automation that reduces operational toil so engineering time goes to product work.
For Terraform Teams
Account Factory for
Terraform (AFT).
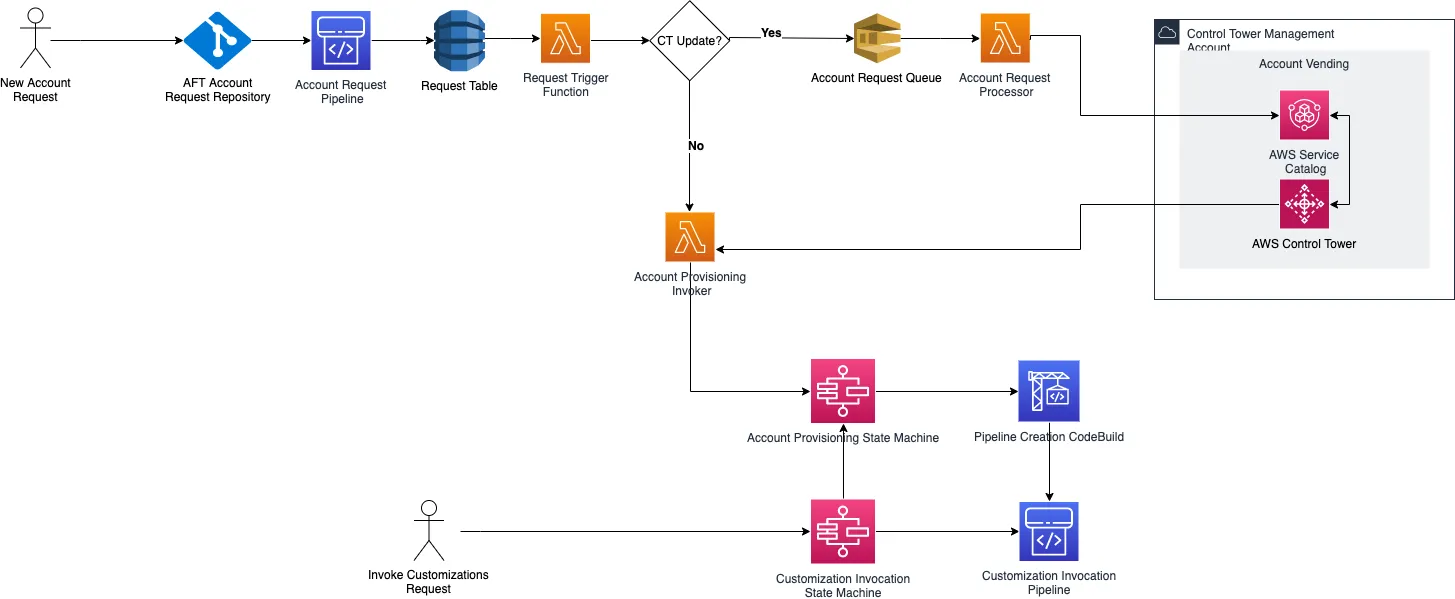
If your organisation already uses Terraform, AFT lets you provision and customise AWS accounts using infrastructure as code, while maintaining all the governance benefits of AWS Control Tower.
GitOps Workflow
Trigger account creation by simply pushing a Terraform file to your Git repo. AFT handles the rest automatically.
Global Customisations
Apply baseline configurations (security, networking, logging) to all accounts (global), specific OUs (targeted), or individual accounts. Version-controlled templates ensure consistency.
Drift Detection
AFT continuously monitors accounts for drift. If someone makes a manual change, AFT automatically corrects it to match your Terraform state.
Why teams partner with Parsectix.
Landing zones are complex. One misstep costs months in remediation. We build enterprise-grade landing zones to AWS best practice, with the aim of getting yours right the first time.
Verified Expertise
AWS Advanced Partner
AWS Advanced Tier Partner with 8 AWS Service Deliveries. We follow AWS Well-Architected Framework and Control Tower best practices to the letter.
Fast Time-to-Value
60-90 Day Delivery
Our phased methodology is designed to shorten typical landing zone timelines. We deploy in phases so you see value immediately, not after months of waiting.
Long-term Partnership
Beyond Deployment
We don’t disappear after launch. Ongoing optimisation, security reviews, and FinOps support ensure your landing zone evolves with your business.
Our proven methodology.
- Step 01
Discovery
We map your current AWS environment, compliance requirements, and business objectives.
- Step 02
Design
Custom landing zone architecture tailored to your security, governance, and operational needs.
- Step 03
Deploy
Phased rollout with Control Tower or AFT. Automated baselines, testing, and validation.
- Step 04
Optimise
Continuous improvement: cost optimisation, security tuning, and operational refinements.
Trusted by teams at
FAQ
Common questions.
Next step
Build your foundation. Scale with confidence.
Don’t let infrastructure complexity slow down your cloud journey. Get a custom landing zone assessment and roadmap from our AWS experts, and we’ll help you get started.
A 30-minute peer conversation, not a sales pitch.